Showing posts with label RFID. Show all posts

Sunday, March 16, 2008

The latest nightmare with RFID

A few days ago, it was reported that one-billion RFID access devices could be compromised by hackers. These devices (using the MiFare RFID chip) are currently deployed as an access device used for mass transit systems, and of far greater concern, secure government facilities.

Please note, ComputerWorld has now revised the estimate of MiFare RFID chips in use to two-billion. For the final tally, we'll have to wait until a more detailed report is published.

According to news sources, this report will be issued on Wednesday.

One person, claiming to be able to hack the RFID devices is a University of Virginia student by the name of Karsten Nohl, according to ComputerWorld. Nohl claims that all he would need now is a latop, scanner and a "few minutes" to start duplicating cards using the chip.

The article cites a computer security consultant, Ken van Wyk of KRvW Associates, as saying at least one European country has dispatched guards to secure facilities where this chip was used in access systems.

From the ComputerWorld article by Sharon Gaudin:

It turns out it's a pretty huge deal," said van Wyk. "There are a lot of these things floating around out there. Using it for building locks is the biggy, especially when it's used in sensitive government facilities — and I know for a fact it's being used in sensitive government facilities."

Van Wyk told Computerworld that one European country has deployed military soldiers to guard some government facilities that use the MiFare Classic chip in their smart door key cards. "Deploying guards to facilities like that is not done lightly," he added. "They recognize that they have a huge exposure. Deploying guards is expensive. They're not doing it because it's fun. They're safeguarding their systems." He declined to identify the European country.

While it probably is a good idea to be very specific about what sensitive government facilties use the card, Engadget mentioned some general places that use this particular RFID chip. They include, "London (Oyster Card, Boston, Netherlands (OV-Chipkaart Minneapolis / St. Paul, South Korea (Upass, T-money, Mybi), Hong Kong, Beijing, Milan, Madrid (Sube-T), Australia (Smartrider), Sao Paulo (Bilhete Unico), Rio de Janeiro (RioCard), Bangkok and New Delhi."

They also put up a YouTube video showing how easily these cards could be compromised. This video was created by the Digital Security section of the Radboud Nijmegen University in the Netherlands.


Full ComputerWorld story on this by Sharon Gaudin, here.

Other posts, I written about RFID nightmares, here.

Tuesday, June 26, 2007

RFID sniffing could be used by spies and criminals to commit all kinds of dastardly deeds!

Dark Reading wrote about a pretty scary flaw in RFID technology this week. Apparently, it's now possible for corporate spies and even organized retail criminal types to "sniff" RFID chips in a cargo container and use the information to commit a dastardly deed.

Apparently, truckers will be particularly vulnerable to being "sniffed" (compromised). Of course, if you use a little imagination, sniffing RFID might put more than "truckers" at risk, also.

From the story in Dark Reading:

That means your competitor could use this information for intelligence purposes. "He could get an idea of what you are shipping and how much, and how often," Perrymon says, adding that an attacker could also write to those tags, either disabling or changing them if you don't apply the proper authorization and passwords to your EPC system. That's PacketFocus's next step in its research.

And sniffing the truck's payload could also provide criminals with intelligence they wouldn’t otherwise be able to get very easily, thus helping them target their holdups or other heists, he says. "Unless they had a lot of inside information, they don't have enough information to rob that truck. Now they can scan it if it's not secure -- they don't want to rob that toilet paper truck, but if it's got plasma TVs with surround sound, [that's their] target."

RFID has been pushed by retailers, such as Walmart, and the military (not mentioned in the Dark Reading article). The Department of Defense now uses RFID to monitor it's supply management system.

Stealing shipments of plasma TVs is one thing, but on a personal level, I'm a little more worried about how some of this technology might be used by those with more sinister intentions than stealing high-tech merchandise.

So far as the passwords mentioned in the article -- easily compromised by the Packet Focus folks, they can be made more secure -- but passwords are hacked by software and more social methods, fairly frequently.

All it takes is one dishonest person with access to one, or even a honest person, who is tricked into giving up one to compromise an entire system.

Hacking for Dummies has an interesting write-up on how passwords are hacked, here.

Besides that, the bad guys are always coming up with new exploits to defeat security fixes.

Interestingly enough, according to Wikipedia, RFID's predecessor was invented by a Soviet inventor as a tool to commit espionage. It also was used the World War II era for a lot of military applications.

Perhaps, in this case, history (or the original intent) should give us a little perspective on RFID?

In the recent past, government experts have seen China show an interest in stealing (hacking) logistics (supply) information. Here is a post, I wrote about that:

How Dangerous is China

Dark Reading's interesting article, here.

I've written a few posts about RFID and it's potential abuses, which can be seen, here.

Dark Reading got it's information for the article from PacketFocus Security Solutions, which is a company that performs what is known as "ethical hacking" for the public at large. Ethical hacking is where good guys test vulnerabilities in technology to stay ahead of the bad guys.

There might very well be some useful applications for RFID, but we need to slow down, and consider the safety implications before continuing to have this technology take over our daily lives.

It's not worth the money a very few people are making off it!

Thursday, April 12, 2007

Sage Predictions on the State of Cyber Crime from McAfee

According to McAfee, cyber crime is growing and as soon as the good guys (white hats) close one loophole, the bad guys (black hats) exploit another.

Unfortunately, technology grows faster than laws and security fixes. Criminals, who are becoming increasingly organized, realize and exploit this fact, frequently.

The report confirms predictions that exploiting VoIP and mobile devices will become more common.

Vishing will probably become more dangerous than phishing - it adds a more personal (voice) touch to tricking people into giving up their personal details. VoIP (cheap long distance) is one of the reasons for this. Since caller-id spoofing is easily available and legal, it makes sense that a lot of people are going to fall victim to vishing attacks.

Also covered is the growth in music and software privacy. Billions of dollars are being lost in both these areas - systems are now being sold with pirated software already installed on them.

To me, this shows how organized, the activity is becoming!

The report also covers RFID technology (quickly becoming commonplace) and how easily it can be exploited. Despite warnings from a lot of concerned experts, we seem to be implementing this technology at a foolish pace (my emphasis).

McAfee deserves recognition for having the courage (there is a lot of money behind RFID technology) to point out the dangers behind this highly profitable, but dangerous (my emphasis), technology.

Enough ranting for the moment, I highly recommend reading the full report, which can be viewed, here.

Tuesday, December 19, 2006

Is Spending $550 Billion on RFID Going to Protect Us?

RFID is making the news again and some prominent politicians are saying we need take a hard look at it before we spend $550 billion (11 billion for each State) implementing it.

RFID is being implemented, or being recomended for implementation (worldwide) to verify a person's identity electronically when identification is presented. And there are people claiming it can already be compromised, or that it is just a matter of time before it will be.

EWeek wrote an interesting article about this about why two of our leaders don't feel RFID is safe, or a wise investment of taxpayer resources:

Sen. Daniel Akaka, D-Hawaii, and Sen. John Sununu, R-N.H., said they take issue with the technological implications of the act.

Sen. Akaka said that if the proposed national database were to be breached it would "provide one-stop access to virtually all information necessary to commit identity theft," and pointed to a study by the National Governors Association estimating that states would have to come up with a total of about $11 billion each to implement the necessary infrastructure to verify information electronically. Akaka will chair the Senate Homeland Security and Governmental Affairs subcommittee the group that has jurisdiction over the relationship between the federal and state governments in 2007.

The Emerging Applications and Technology Subcommittee, part of the Data Privacy and Integrity Committee that advises DHS, toned down its harsh criticisms of RFID technology used to identify individuals referring to the e-passport and PASScard ID card in a report released Dec. 13.

EWeek story, here.

And in another story a few thousand miles away from Washington, an Aussie hacker is claiming he can already hack Australian and British passports.

Sydney Morning Herald story, here.

Technology, including RFID is making people billions of dollars. Unfortunately, there is growing evidence that RFID isn't 100 percent secure. If RFID is easily hacked, there will be other (or maybe the same people) making a lot of money selling "security" to protect people from it.

Tracking inventory in Walmart's supply chain is one thing, but tracking humans is something that needs to be thought out, carefully. And $550 billion is a huge expenditure of the taxpayer's hard-earned money! We need to ensure this is a wise investment and that that individual privacy doesn't suffer because of it.

You can read Senator Akaka's press release on this subject, here.

And to go to Senator Sununu's page (couldn't find a release about RFID yet), click here.

For my previous posts on this subject, click here.

Wednesday, October 25, 2006

Are RFID Credit Cards Safe?

The RFID ConsortiUm for Security and Privacy (CUSP) has issued a study about vulnerabilities in first-generation RFID-enabled credit cards.

In their blog, Ari Juels writes:

Consumers in the United States today carry some twenty million or so credit cards and debit cards equipped with RFID (Radio-Frequency IDentification) chips. RFID chips communicate transaction data over short distances via radio. They eliminate the need to swipe cards or hand them to merchants. Consumers can instead make payments simply by waving their cards—or even just their wallets—near point-of-sale terminals.

While appealing to both consumers and merchants, the convenience of RFID credit cards has a flip side. What a legitimate merchant terminal can read, a malicious scanning device can also read without a consumer’s consent or knowledge. RFID credit cards therefore call for particularly careful security design.

Blog post, here.

In a "nutshell," the study warns that current RFID credit cards are vulnerable to having the identities of the cardholder scanned from afar and the information could also be used in credit/debit card skimming.

They also state that this can be accomplished without great technical difficulty and that "slightly stronger data protections and cryptography would largely prevent the problems they discovered."

The study admits that "card skimming" is already a big problem, therefore these cards are unlikely to change anything that isn't already going on.

My question is when will we start developing technology that will protect the consumer instead of developing technology that will "probably" add to the problem?

There is an interesting demonstration posted by RFID-CUSP on YouTube about this, here.

Here is a previous post, I did on RFID:

RFID, A Necessary Evil; or an Invasion of Privacy?

Sunday, August 06, 2006

Expert Warns RFID Passports AREN'T Completely Safe

Looks like a lot of "information" is coming out from the "Hackers Convention" (DefCon) in Vegas. Here - AGAIN - an expert is warning that using RFID in passports might have security implications.

Here is an interesting article from Dan Goodin of the AP:

Electronic passports being introduced in the U.S. and other countries have a major vulnerability that could allow criminals to clone embedded secret code and enter countries illegally, an expert warned.

A demonstration late Friday by German computer security expert Lukas Grunwald showed how personal information stored on the documents could be copied and transferred to another device.

It appeared to contradict assurances by officials in government and private industry that the electronic information stored in passports could not be duplicated.

Link to AP article, here.

Here is a recent post, I wrote about another warning concerning the use of RFID in passports:

RFID Hacked Again and Vendor Says it's as Safe as Anything in Your Wallet!

Saturday, March 11, 2006

How Dangerous is China

David Perera of GovExec.com wrote an interesting piece deducting that Chinese hackers might be more interested in hacking our logistic systems than more classified systems that the military uses.

David Perera writes:
For Americans today, war evokes images of roadside bombs and hidden snipers in the Middle East. But Defense Department planners who are paid to think about future wars worry about the People's Republic of China. Rising powers long have challenged dominant countries for primacy - it's an old story. And now, nobody is more powerful than the United States.

Logistics information literally is the bread and butter of the military. Track the supply lines of materiel and personnel and you'll know where troops are headed. Disrupt that supply line, and you will have created a barrier to getting there quickly. Amateurs study tactics, professionals study logistics, goes the Pentagon cliché. Yet great chunks of logistics information flow across the unclassified Defense Department system, the Nonsecure Internet Protocol Router Network, or NIPRNet. The Pentagon maintains a separate network for secret information, but the NIPRNet is its daily workhorse.

The world's largest network once was one built from flagstone-paved roads extending 53,000 miles in Roman antiquity. The roads were designed as a tool for policing an empire, and also for trade and communications. Unfortunately for the Romans, barbarians found them equally useful for their own purposes - attacking legionnaires - and eventually the Roman Empire was no more.
Full story, here.

Last November, I wrote about, US Military Hacked, Sober Worm Goes Worldwide, What Next?

"The Chinese (who seem to be behind the most recent attack on the military) have been suspected of selling technology (including nuclear) to governments, who might be dangerous to world peace. All one has to do is read the story of AQ Khan, who developed nuclear weapons for Pakistan and admitted selling secrets to North Korea, Libya and Iran. There is a lot of speculation that he obtained a lot of his knowledge from the Chinese, who were caught stealing nuclear secrets from us during the Clinton Administration, Online NewsHour: Spies Among Us -- June 9, 1999."

There is also a lot of other evidence that the Chinese are heavily involved in cyber-espionage activities. The FBI Computer Crime Survey stated that China was responsible for 23.9% of the cyber attacks in their survey.

Of course, the United States is still the number one source, but one has to consider that the internet is heavily censored in China. This would lead a logical person to come to the conclusion that certain activities are being tolerated by those, who censor it.

In fact, some have dubbed it the "Great Firewall of China."

Another factor to consider is organized criminal activity of Chinese origin:

Chinese Criminal Enterprises - US Department of State

One of the activities, they are actively involved in is "illegal immigration," which could provide a conduit for planting spies in the industrial and financial sectors.

Patrick Devenny of FrontPage.com recently wrote a story, where he quoted Sun Tzu from the Art of War:

Foreknowledge cannot be gotten from ghosts and spirits, cannot be had by analogy, cannot be found out by calculation. It must be obtained from people, people who know the conditions of the enemy.

In his article, he writes:

The list of additional recent Chinese espionage cases is long and disturbing. It includes, among others, the theft of Blackhawk helicopter engines and optical devices by a South Korean man arrested last year. A Chinese-American couple in Wisconsin was arrested in 2004 for sending over $500,000 worth of computer parts to the Chinese government that can be used to improve missile guidance systems.

Statements from officials such as Szady hint that cases like these are just a small sample of the overall secret Chinese war against America. Indeed, in the words of one unnamed senior FBI source, “the Chinese are stealing us blind, the 10 year technological advantage we had is vanishing.”

Daily, we read of the threat from Terrorism. While this isn't an issue to be ignored, we can't afford to ignore what seems to be an ongoing and calculated threat from China.

AND there could be more ominous implications. One of the biggest threats today is the possibility of Iran becoming a nuclear power.

Guess who has been providing them with technology that could have stolen from us-China (courtesy of NTI).

Sunday, October 30, 2005

RFID, Abuse in the Private Sector?

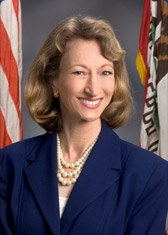
"How would you like it if, for instance, one day you realized your underwear was reporting on your whereabouts?" California State Senator Debra Bowen (pictured on right).

RFID (Radio Frequency ID) has hit the news with the technology being introduced into U.S. passports. Because of this, I decided to research the controversy and did so in a previous post: RFID, A Necessary Evil; or an Invasion of Privacy?

This second post is meant to focus on the privacy issues (controversies) that surround this product. While this technology has definite security and supply chain potential, the potential for abuse is also great.

I suppose the use of these tags is inevitable, however we need to be proactive in developing legislation (laws) designed to prevent their abuse. Legislation rarely keeps up with technology and from a historical perspective there has been substantial abuse of other technologies, such as adware/spyware and keyloggers; which have been used for illegal purposes and legally (because of a lack of legislation) to invade personal privacy.

Simson L. Garfinkel wrote an article about this in "The Nation." Here are some excerpts:

So why did the American Civil Liberties Union, the Electronic Frontier Foundation, The World Privacy Forum and a dozen other organizations ask for a voluntary moratorium on RFID technology in consumer goods? Because this use of RFID could enable an omnipresent police surveillance state, it could erode further what's left of consumer privacy and it could make identity theft even easier than it has already become.

RFID is such a potentially dangerous technology because RFID chips can be embedded into products and clothing and covertly read without our knowledge. A small tag embedded into the heel of a shoe or the inseam of a leather jacket for inventory control could be activated every time the customer entered or left the store where the item was bought; that tag could also be read by any other business or government agency that has installed a compatible reader. Unlike today's antitheft tags, every RFID chip has a unique serial number. This means that stores could track each customer's comings and goings. Those readers could also register the RFID tags that we're already carrying in our car keys and the "prox cards" that some office buildings use instead of keys.

Mr. Garfinkel's conclusion, which seems very sound, was:

Companies that are pushing RFID tags into our lives should adopt rules of conduct: There should be an absolute ban on hidden tags and covert readers. Tags should be "killed" when products are sold to consumers. And this technology should never be used to secretly unmask the identity of people who wish to remain anonymous.


For the complete article by Mr. Simpson, go to: The Nation: The Trouble with RFID.

Again, I used my friends at "Wikipedia" to find some examples of potential abuse that has already occurred:

The potential for privacy violations with RFID was demonstrated by its use in a pilot program by the Gillette Company, which conducted a "smart shelf" test at a Tesco in Cambridge. They automatically photographed shoppers taking RFID-tagged safety razors off the shelf, to see if the technology could be used to deter shoplifting.

In another study, uncovered by the Chicago Sun-Times, shelves in a Wal-Mart in Broken Arrow, Oklahoma, were equipped with readers to track the Max Factor Lipfinity lipstick containers stacked on them. Webcam images of the shelves were
viewed 750 miles (1200 km) away by Procter & Gamble researchers in Cincinnati, Ohio, who could tell when lipsticks were removed from the shelves and observe the shoppers in action.

In January 2004 a group of privacy advocates was invited to METRO Future Store in Germany, where an RFID pilot project was implemented. It was uncovered by accident that METRO "Payback" customer loyalty cards contained RFID tags with customer IDs, a fact that was disclosed neither to customers receiving the cards, nor to this group of privacy advocates. This happened despite assurances by METRO that no customer identification data was tracked and all RFID usage was clearly disclosed.

The controversy was furthered by the accidental exposure of a proposed Auto-ID consortium public relations campaign that was designed to "neutralize opposition" and get consumers to "resign themselves to the inevitability of it" whilst merely pretending to address their concerns.

The standard proposed by EPC global includes privacy related guidelines
for the use of RFID-based EPC. These guidelines include the requirement to give consumers clear notice of the presence of EPC and to inform them of the choice that they have to discard, disable or remove EPC tags. These guidelines are non-binding, and only partly comply with the joint statement of 46 multinational consumer rights and privacy groups.

If readers are easily accessible, or not protected properly from theft, there is also the potential that identity thieves could scan personal information. Whether or not, this is feasible is a matter of great debate, but as with all technology, even if it isn't feasible now, how long will it take for someone to create a way to do it?

Friday, October 28, 2005

RFID, A Necessary Evil; or an Invasion of Privacy?

With the State Department's (United States) announcement of adding RFID (Radio Frequency ID) chips to passports, the controversies surrounding this technology are again making headlines. Please note that other countries, especially in the European Union are also implementing RFID technology for identification purposes.

The Pakistan Passport Authority is already using RFID tags in it's passports. This might be an interesting place to study it's effectiveness because Pakistan seems to continue to be a sanctuary for terrorists and is known to be a origin and transshipment point for a lot of drug smuggling.

In recent years, RFID has been the "buzz word" in the security industry, however there are those that challenge it's long-term effectiveness. There are also those who fear that it will be abused, violating our rights to privacy and even other's from the religious community, who fear RFID is the mark of the beast mentioned in the Book of Revelation (Revelation 13:16).

The definition of RFID in Wikipedia is "an automatic identification method, relying on storing and remotely retrieving data using devices called RFID tags or transponders. An RFID tag is a small object that can be attached to or incorporated into a product, animal, or person. RFID tags contain antennas to enable them to receive and respond to radio-frequency queries from an RFID transceiver. Passive tags require no internal power source, whereas active tags require a power source."

The proverbial question is RFID a necessary means of protecting ourselves, or in the end will the technology be abused to violate privacy, such as spyware and adware have already done.

This technology has been around for awhile. Currently, Wal-Mart and the United States Department of Defense are using this technology to manage their supply chains, as well as, prevent pilferage and theft. With decreasing costs, we can expect to see a lot more of this technology deployed by both the private and public sectors in the near term.

Besides being used for identification, RFID tags are being used as quick pay devices for fuel and tolls, theft tracking devices, to track animals and there have even been some implanted in humans.

Some of the security concerns already raised are if the ability to read them is too universal, they could pose a risk to personal location privacy, especially in the corporate/military environments. Another concern being raised by privacy groups are RFID devices being embedded in products (which aren't removed when purchased) that could be tracked from great distances. Because of this, they could be used for so-called "marketing" purposes, which invade personal privacy.

There are also concerns that these "tags" could be cloned.

If these tags could be cloned, they could be used in producing false identification, which is alarming considering the technology is being used for high security applications like "proximity cards used to access secure facilities, or vehicle immobilizer anti-theft systems which use an RFID tag embedded in the vehicle key. It is also a problem when RFID is used for payment systems, such as contactless credit cards (Blink, ExpressPay), the ExxonMobil Speedpass, and even in RFID enhanced casino chips."

"With wireless technology, RFID tags can be scanned from afar. Because of this, there is even more potential for abuse than the reencoding of magnetic stripe technology. There are defenses built into these tags, which fall into two categories. There are those use "cryptographic protocols. A typical example of the "RF-based" defense relies on the fact that passive RFID tags can only be activated by a reader in close proximity, due to the limited transmission range of the magnetic field used to power the tag. RFID manufacturers and customers occasionally cite this limitation as a security feature which (intentionally or otherwise) has the effect of limiting scanning range. However, while this approach may be successful against direct tag scanning, it does not necessarily prevent "eavesdropping" attacks, in which an attacker overhears a tag's response to a nearby, authorized reader. Under ideal conditions, these attacks have proven successful against some RFID tags at a range of more than sixty feet."

"A second class of defense uses cryptography to prevent tag cloning. Some tags use a form of "rolling code" scheme, wherein the tag identifier information changes after each scan, thus reducing the usefulness of observed responses. More sophisticated devices engage in challenge-response protocols where the tag interacts with the reader. In these protocols, secret tag information is never sent over the insecure communication channel between tag and reader. Rather, the reader issues a challenge to the tag, which responds with a result computed using a cryptographic circuit keyed with some secret value. Such protocols may be based on symmetric or public key cryptography. Cryptographically-enabled tags typically have dramatically higher cost and power requirements than simpler equivalents, and as a result, deployment of these tags is much more limited. This cost/power limitation has led some manufacturers to implement cryptographic tags using substantially weakened, or proprietary encryption schemes, which do not necessarily resist sophisticated attack."

Last, but not least, there are "social" factors to be considered. Even with the best technology available, we have seen many technologies "hacked" that are supposed to protect us today. In the past couple of years, we have also seen massive data intrusions, many of which were accomplished by simple theft and or insider collusion.

In fact, a lot of the organized gangs committing fraud today, have access to a lot of displaced "highly educated" computer scientists, which already assist them in hacking technology at every turn for their criminal purposes. This is especially true of the area, formerly known as the Soviet Union, where a lot of these gangs are based.

One of the reasons, we are considering this technology is certainly the 9-11 attacks. We can implement the best technology available, however unless it is worldwide, the "bad and the ugly" will be able to obtain identification based on other identification. In fact several of the 9-11 attackers did just this in Virginia. In other words, it probably wouldn't have made any difference if RFID technology was in place in the 9-11 disaster.

Technology is merely a tool. Even though it continues to amaze me at how quickly it advances, it doesn't replace the human mind. While RFID technology is a tool to use for our protection, we must continue to examine, whether or not, it has potentials for abuse.